NAT incoming FTP traffic to an FTP server
This task enables you to redirect external FTP traffic to an internal FTP server by creating a static NAT rule that maps the external interface to the internal server.
Use this procedure when you need to allow external users to access an internal FTP server through your firewall. The NAT rule translates the public interface address to the private FTP server address.
Procedure
Step 1 | In the left pane, click . |
Step 2 | Click the Devices tab to locate the device or the Templates tab to locate the model device. |
Step 3 | Click the appropriate device type tab. |
Step 4 | Select the device you want to create the NAT rule for. |
Step 5 | Click NAT in the Management pane at the right. |
Step 6 | Click |
Step 7 | In section 1, Type, select Static. Click Continue. |
Step 8 | In section 2, Interfaces, choose inside for the source interface and outside for the destination interface. Click Continue. |
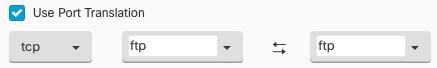
Step 9 | In section 3, Packets, perform these actions:
|
Step 10 | Skip section 4, Advanced. |
Step 11 | For an FDM-managed device, in section 5, Name, give the NAT rule a name. |
Step 12 | Click Save. The new rule is created in section 2 of the NAT table. |
Step 13 | Review and deploy now the changes you made, or wait and deploy multiple changes at once. |

Entries in the ASA's Saved Configuration File
Here is the entry that is created and appears in the ASA's saved configuration file as a result of this procedure.
Note | This does not apply to FDM-managed devices. |
Object created by this procedure
object network ftp-object
host 10.1.2.27
NAT rule created by this procedure
object network ftp-object
nat (inside,outside) static interface service tcp ftp ftp