NAT incoming HTTP traffic to an HTTP server
Create a network object NAT rule that translates inbound traffic, bound for a static IP address and port, to an internal address when you only have one public IP address or a very limited number.
If you only have one public IP address, or a very limited number, you can create a network object NAT rule that translates inbound traffic, bound for a static IP address and port, to an internal address. We have provided procedures for specific cases, but you can use them as a model for other supported applications.
Before you begin
Before you begin, create a network object for the HTTP server. For the sake of this procedure, we will call the object, HTTP-object.
See Create Network ObjectsCreate Network Objects for instructions.
Follow these steps to NAT incoming HTTP traffic to an HTTP server:
Procedure
Step 1 | In the left pane, click . |
Step 2 | Click the Devices tab to locate the device or the Templates tab to locate the model device. |
Step 3 | Click the appropriate device type tab. |
Step 4 | Select the device you want to create the NAT rule for. |
Step 5 | Click NAT in the Management pane at the right. |
Step 6 | Click |
Step 7 | In section 1, Type, select Static. Click Continue. |
Step 8 | In section 2, Interfaces, choose inside for the source interface and outside for the destination interface. Click Continue. |
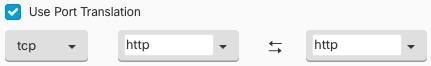
Step 9 | In section 3, Packets, perform these actions:
|
Step 10 | Skip section 4, Advanced. |
Step 11 | For an FDM-managed device, in section 5, Name, give the NAT rule a name. |
Step 12 | Click Save. The new rule is created in section 2 of the NAT table. |
Step 13 | Review and deploy now the changes you made, or wait and deploy multiple changes at once. |

Entries in the ASA's Saved Configuration File
Here are the entries that are created and appear in an ASA's saved configuration file as a result of this procedure.
Note | This does not apply to FDM-managed devices. |
Object created by this procedure
object network http-object
host 10.1.2.28
NAT rule created by this procedure
object network http-object
nat (inside,outside) static interface service tcp www www