How Splunk Federated Search Integrates with Cisco Security Analytics and Logging
Splunk Federated Search integration with Cisco Security Analytics and Logging is a cloud-native security architecture that
-
enables federated search queries from Splunk Cloud Platform to access security event data in Cisco Security Analytics and Logging without local data ingestion
-
leverages token-based authentication to authorize data access between the platforms, and
-
centralizes security event visibility through Security Cloud Control for unified security management across hybrid and multicloud environments.
Integration components and data flow
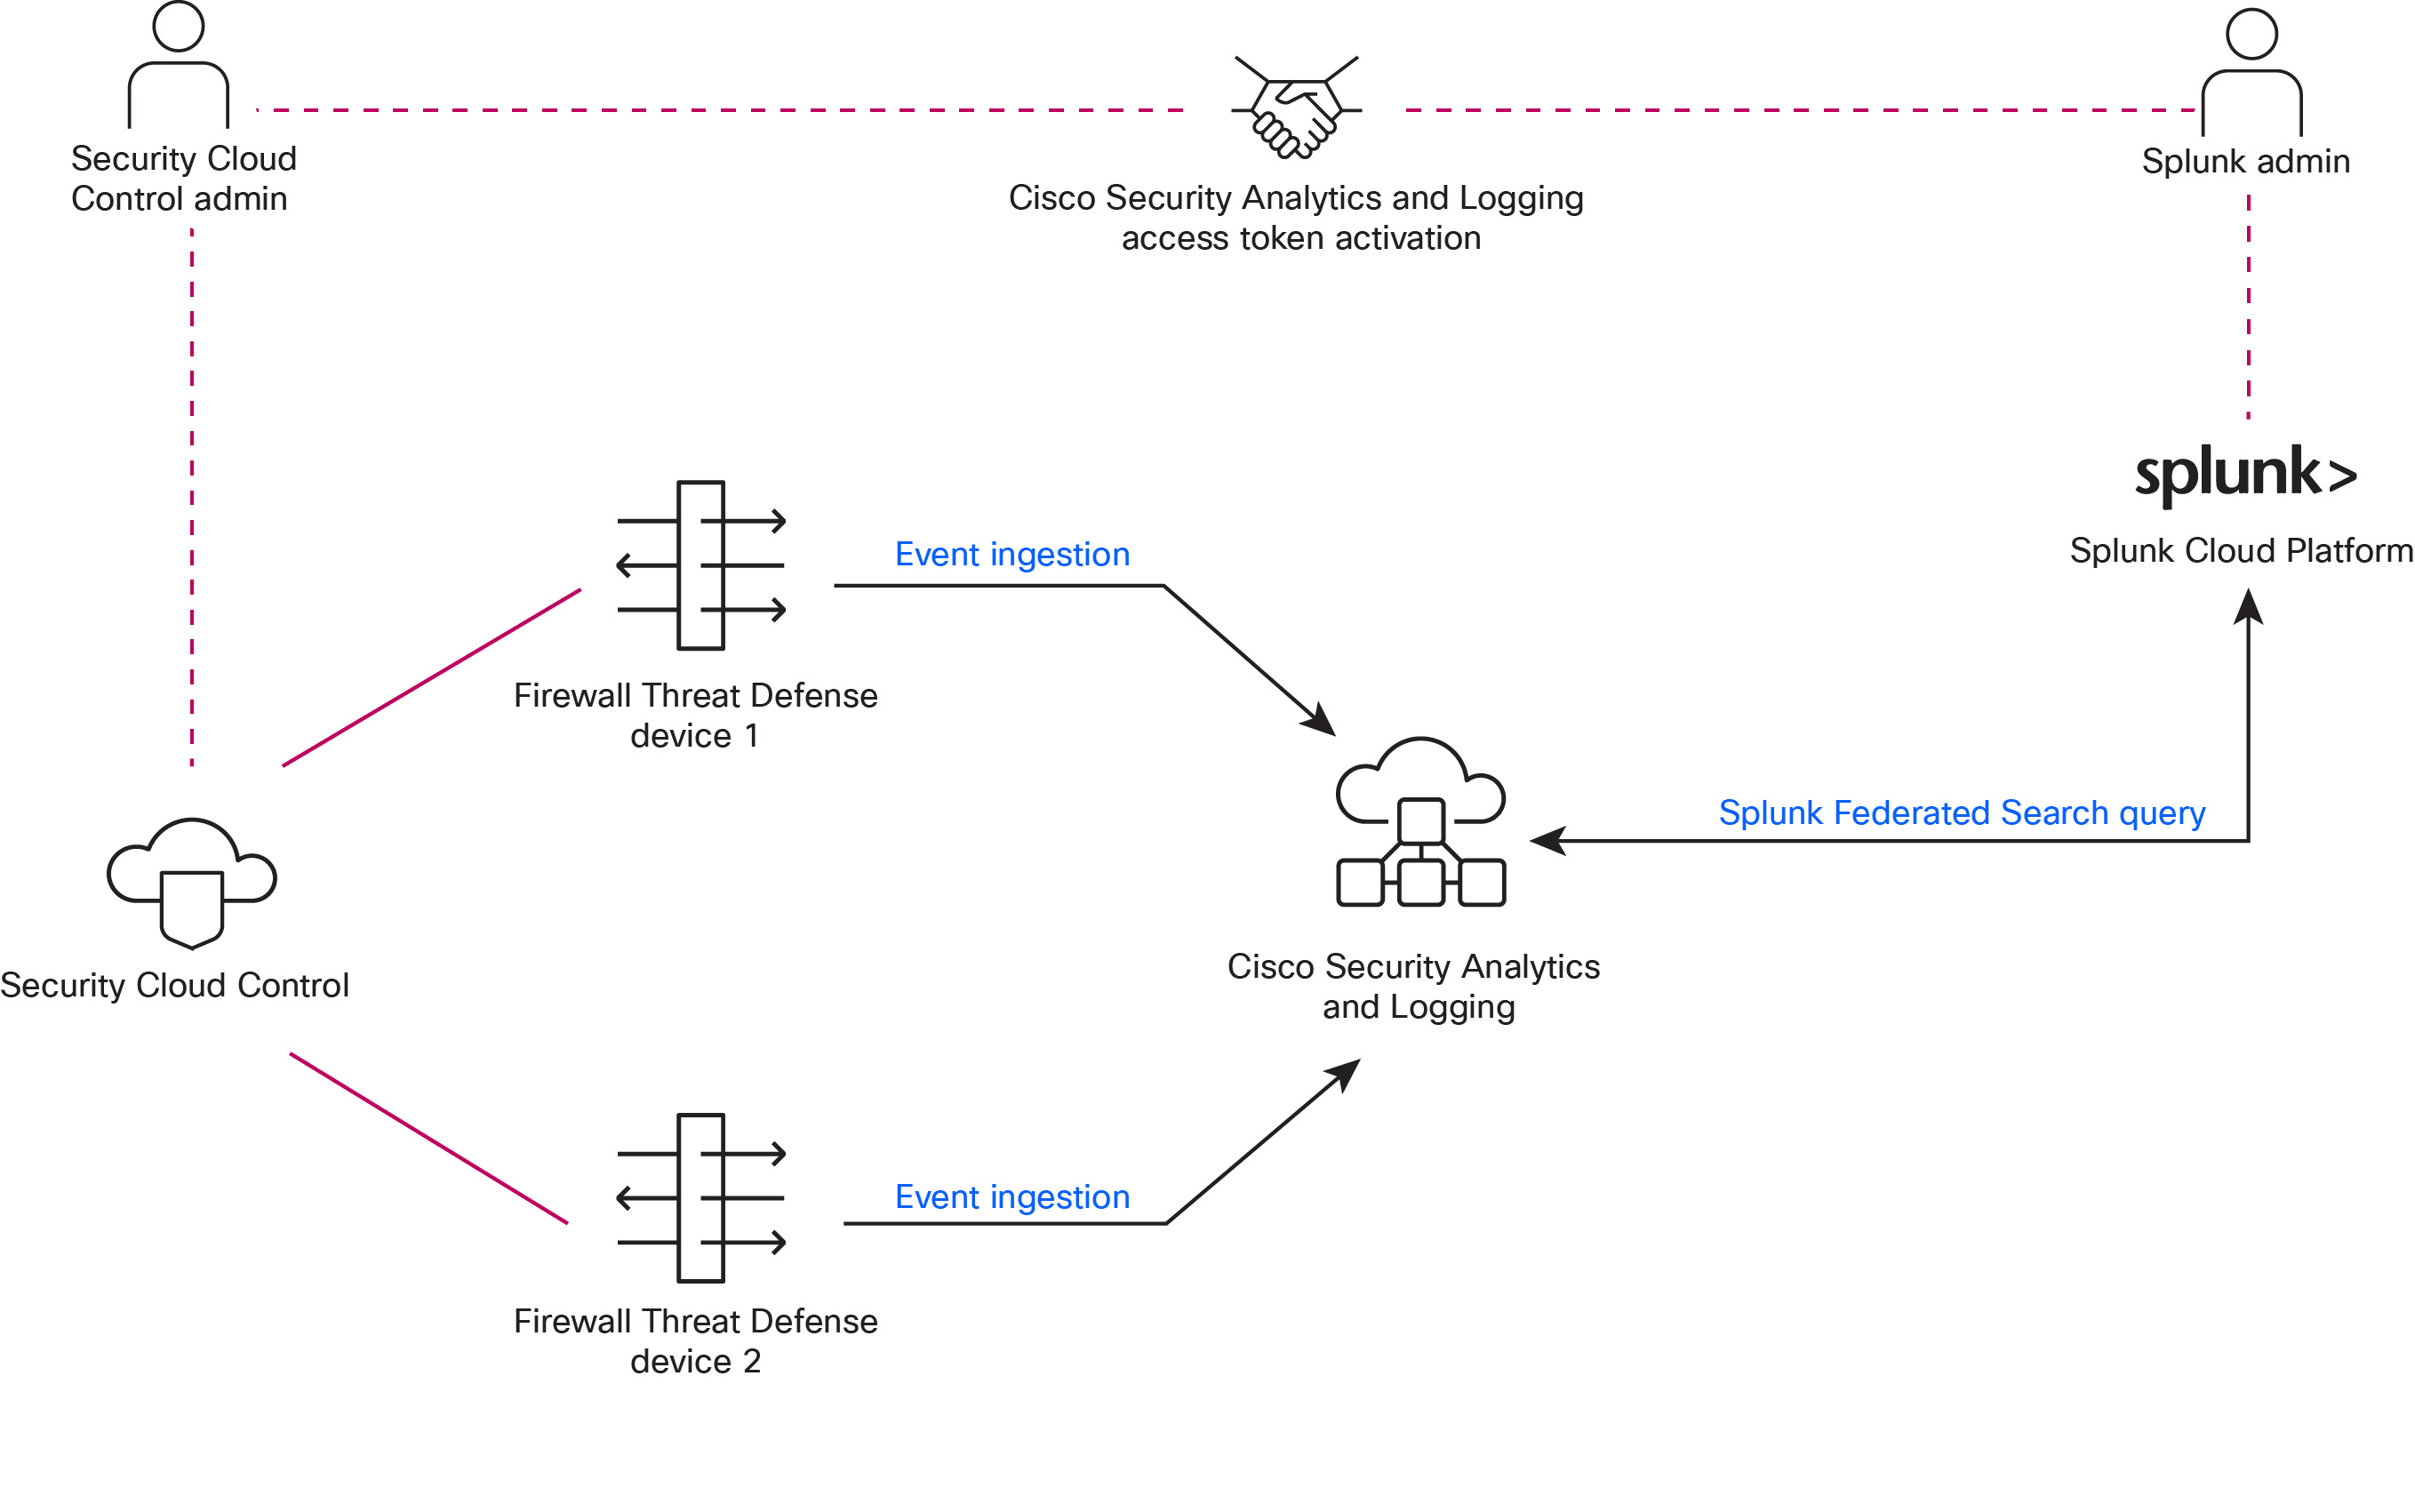
This topology shows the flow of information and interactions between the following components:
-
Security Cloud Control: A unified, cloud-native security management interface designed to centralize and simplify the management of Cisco security solutions across hybrid and multicloud environments. It leverages Cisco Security Analytics and Logging to provide visibility into security events and trends.
-
Cisco Security Analytics and Logging: This cloud-based platform serves as a central repository for aggregated security event data from various sources, including the Cisco Secure Firewall Threat Defense devices. It ingests event logs from these devices and allows Splunk Federated Search to query this event data.
-
Security Cloud Control admin: This administrator manages the Security Cloud Control platform, overseeing the configuration and operational status of security devices like firewalls. They are responsible for setting up the necessary integrations, including the activation of the access token for Cisco Security Analytics and Logging.
-
Cisco Security Analytics and Logging token activation: A access token-based mechanism is employed to authenticate and authorize Splunk and Cisco Security Analytics and Logging service interactions. It ensures that event data in Cisco Security Analytics and Logging can be queried by Splunk Federated Search.
-
Splunk admin: This administrator is responsible for managing the Splunk environment and leveraging its capabilities for security analysis. The admin configures and initiates federated searches to query and retrieve security event data from external platforms, such as Cisco Security Analytics and Logging, without needing to ingest all data locally.
-
Splunk Federated Search query: This refers to the query initiated from Splunk Cloud platform to access and analyze data residing in Cisco Security Analytics and Logging. All Firewall Threat Defense security events can be queried from the Splunk Cloud Platform.
-
Splunk Cloud Platform: This represents the Splunk Security Information and Event Management (SIEM) platform, which utilizes its federated search capability to integrate with Cisco Security Analytics and Logging. This integration allows the security teams to query event data from Cisco Security Analytics and Logging without needing to ingest data locally.